Why App Security Should Be a Priority From Day One
When businesses decide to build a mobile app or web application, they usually focus on the features users will see. They think about the design, navigation, performance, and how the app will help their customers.
These things matter, but there is another important part of development that often receives attention too late: security.
An application may look excellent and work perfectly during testing, but that does not automatically mean it is secure. If user accounts are poorly protected, APIs expose sensitive information, or database access is not properly controlled, the application can become vulnerable.
Security should not be treated as a final checklist before launch. It should be part of the development process from the beginning.
Whether you are building a small business application, an e-commerce platform, a family organizer, or a large social networking app, security decisions made during development can have a lasting impact on the product.
1. Protecting User Information
Most modern applications collect or process some form of user information. This might include names, email addresses, phone numbers, profile photos, messages, preferences, or account activity.
Depending on the application's purpose, it may also handle addresses, payment-related information, or other sensitive data.
Users expect this information to be handled responsibly. They trust an application to protect their accounts and only use their data for appropriate purposes.
If an application collects more information than it needs or stores that information without suitable protection, it increases the potential consequences of a security incident.
A better approach starts with a few simple principles:
-
Collect only the information the application genuinely needs.
-
Restrict access to sensitive data.
-
Protect information while it is transmitted and stored.
-
Avoid exposing personal information through logs, error messages, or API responses.
-
Define how long information should be retained and when it should be deleted.
Good data protection is not just a technical decision. It is also part of building a trustworthy relationship with users.
2. Secure Authentication and Account Access
Authentication is the process of confirming a user's identity. It commonly involves an email and password, an OTP, or an approved sign-in provider.
However, having a login screen does not automatically make an application secure.
Developers must also consider how credentials are handled, how sessions are managed, and what happens when a user logs out or loses access to an account.
For example, an application should not rely only on hiding a screen in the frontend to prevent unauthorized access. The backend must verify the user's identity before allowing access to protected information or actions.
A secure authentication system should consider:
-
Safe password storage using established password-hashing methods.
-
OTP expiration and attempt limits.
-
Appropriate session or token expiration.
-
Secure storage of authentication tokens on the device.
-
Protection against repeated login attempts.
-
Reliable logout and account-revocation behavior.
-
Additional verification for sensitive account changes when appropriate.
These details may not be visible to users, but they make a significant difference to the application's security.
3. Why Backend Security Matters
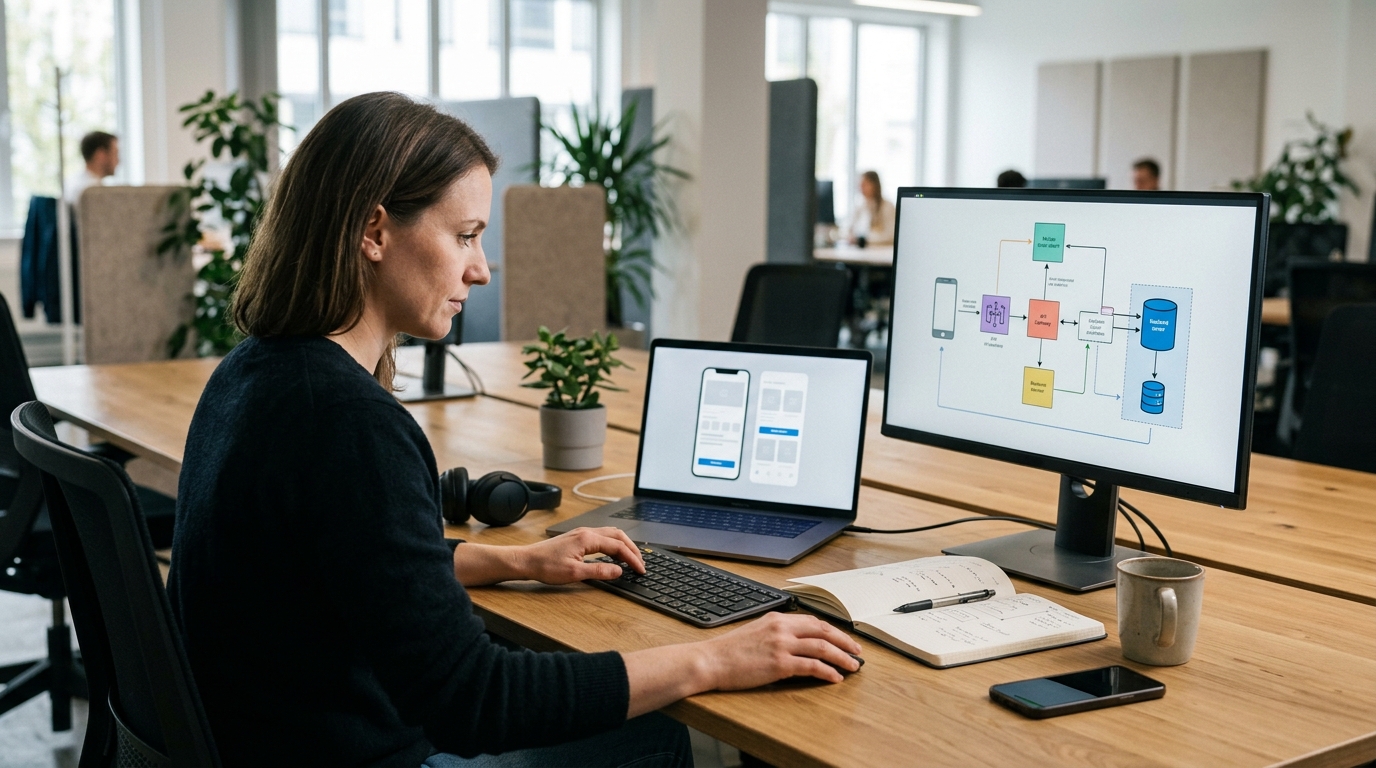
A mobile application is only one part of a larger system. Behind the interface, the backend often manages authentication, business logic, user information, notifications, and communication with the database.
If the backend is poorly secured, even a well-designed mobile application can be exposed to risks.
Consider a simple example: a user opens a profile screen and sees their own information. The application sends a request to the backend, which retrieves the relevant record.
The backend must confirm that the authenticated user is allowed to access that record. It should never trust a user ID supplied by the app without checking the user's permissions.
Without proper authorization, someone might attempt to change a request parameter and access another person's information.
This is why backend development requires more than making APIs work. Each protected operation needs appropriate authentication, authorization, input validation, and error handling.
Security must be enforced on the server, where access decisions can be checked consistently.
4. Protecting APIs and Database Access
APIs allow mobile apps, websites, and other systems to communicate with a backend. They are essential to modern application development, but they also need careful protection.
An API endpoint that returns information without checking permissions may expose data to unauthorized users. An endpoint that accepts unvalidated input may create opportunities for abuse or unexpected behavior.
Developers should review API security throughout development.
Important practices include:
-
Requiring authentication for protected endpoints.
-
Checking permissions for individual records and actions.
-
Validating incoming data on the server.
-
Applying rate limits where appropriate.
-
Using parameterized database queries or safe ORM query methods.
-
Returning only the fields the client actually needs.
-
Avoiding sensitive information in error responses.
-
Keeping secrets and private credentials out of application code.
Database credentials should never be embedded in a mobile app. Mobile applications can be inspected, so secrets included in the app package should not be considered private.
Instead, the backend should manage database access through controlled server-side configuration and appropriate permissions.
These measures help reduce the risk of unauthorized access and misuse.
5. Secure Data Transmission and Storage
Information frequently moves between an application, its backend, third-party services, and databases. Every connection should be considered when designing a secure system.
HTTPS should be used to protect data transmitted between clients and servers. Production services should use correctly configured TLS certificates and avoid insecure connections.
Local storage requires similar attention. Applications often save authentication tokens, user preferences, cached content, or temporary files on a device.
Not all information needs the same level of protection. Public preferences may require little protection, while authentication credentials and sensitive personal data require much stronger controls.
For mobile applications, developers should use platform-appropriate secure storage for sensitive credentials and avoid placing secrets in ordinary preferences, source code, or debug logs.
Backups, crash reports, analytics tools, and third-party integrations should also be reviewed because they may handle information outside the main application.
Security is strongest when developers understand the full journey of the data rather than focusing only on the main database.
6. Security Should Be Part of the Development Workflow
One common mistake is to postpone security testing until the application is almost ready for release.
By that point, important architectural decisions may already be difficult or expensive to change. A rushed review may also miss problems hidden in less frequently used features.
A more effective approach is to include security checks throughout development.
During planning, identify the information the application handles and the potential risks. During implementation, follow secure coding practices and apply access controls. During testing, examine authentication, permissions, validation, and error handling.
Before release, review production configuration, dependencies, logging, and any external services that process user information.
Security reviews should continue after launch because applications evolve. New features, changing dependencies, and new integrations can introduce risks that did not exist in earlier versions.
A consistent workflow makes security a shared responsibility rather than a task left to the final stage.
7. Testing Helps Identify Problems Before Launch
Even experienced developers can introduce security weaknesses. Testing helps identify issues before they affect real users.
Security testing should cover more than whether users can log in successfully. It should also examine what happens when users try actions they are not authorized to perform.
For example:
-
Can one user access another user's private records?
-
Does the backend reject expired or invalid authentication tokens?
-
Are repeated OTP requests limited appropriately?
-
Does the API validate unexpected or malformed input?
-
Are sensitive fields excluded from public responses?
-
Can a user access administrative functionality without the correct role?
-
Are errors handled without revealing secrets or internal implementation details?
Automated tests can help catch recurring problems, while manual reviews and appropriate security testing can reveal issues that ordinary functional tests may overlook.
Testing should always be performed within an authorized environment and with suitable test data.
8. Third-Party Services Need Attention Too
Modern applications often depend on external services for analytics, cloud storage, push notifications, payments, authentication, maps, or AI features.
These integrations can save development time, but they also introduce additional security and privacy considerations.
Before adding a service, developers should understand what information it receives, how its credentials are protected, and what permissions it requires.
API keys intended for public client-side use should be restricted appropriately. Secret keys must remain on trusted server infrastructure. Access permissions should follow the principle of least privilege, meaning each service receives only the access it needs.
Developers should also review dependencies and update them when security fixes become available.
Using a popular framework or trusted provider does not eliminate the need for secure configuration. Every integration becomes part of the application's overall security picture.
9. Security Supports Long-Term Business Growth
Security is sometimes viewed as an extra development cost. In reality, planning for security early can help avoid expensive redesigns and reduce operational risks later.
Imagine an application that launches without proper role-based permissions. As the number of users grows, the business adds administrators, moderators, premium accounts, and private content.
If the original system does not support reliable permission checks, developers may need to redesign important parts of the backend before these features can be introduced safely.
By considering security during the initial architecture, teams can build a foundation that supports new features without repeatedly rebuilding core systems.
Strong security practices can also help businesses demonstrate responsible data handling, meet applicable requirements, and maintain user confidence.
Security does not guarantee that an application will never experience an incident. However, sensible preparation can reduce exposure and make problems easier to detect, investigate, and manage.
10. What Businesses Should Ask Before Launching an App
If you are planning to launch an application, you do not need to understand every technical detail to ask useful questions.
Start by asking your development team how user accounts are protected, how access to private information is controlled, and how the backend validates requests.
Ask whether sensitive credentials are stored securely, whether the application uses HTTPS, and how security issues are tested before release.
It is also worth discussing backups, dependency updates, monitoring, incident response, and who will maintain the application after launch.
The answers should reflect the actual needs of the product. A small internal tool and a financial application will not have identical security requirements, but both should receive appropriate protection for the information they handle.
Clear conversations about security help businesses make informed decisions before problems occur.
Conclusion
A successful application needs more than attractive screens and useful features. It also needs a reliable foundation that protects user accounts, manages data responsibly, and prevents unauthorized access.
Authentication, backend authorization, secure APIs, protected data storage, testing, and careful third-party integration all contribute to that foundation.
The best time to consider these practices is at the beginning of development, when the architecture is being planned and the core systems are taking shape.
At GoTech Studio, we believe that building dependable software means thinking about performance, usability, maintainability, and security together.
If you are planning a new mobile app or improving an existing product, make security part of the conversation from day one.
Ready to build a reliable application for your business? Visit https://gotechstudio.com/ to explore our development services.